
Acme Analytics | Turning Security Noise into Decision-Ready Intelligence
Security teams face an overwhelming volume of alerts, fragmented tools, and limited context - making it hard to identify what truly matters.
Role
Lead UX Manager
Timeline
16 weeks · 2025
Team
4 UX Designers
2 UX Researchers
1 UX Writer
1 Product Director
2 Security SMEs
1 Product Engineer
Primary metric
46% ↓ alert noise
$2.1M+ annual savings
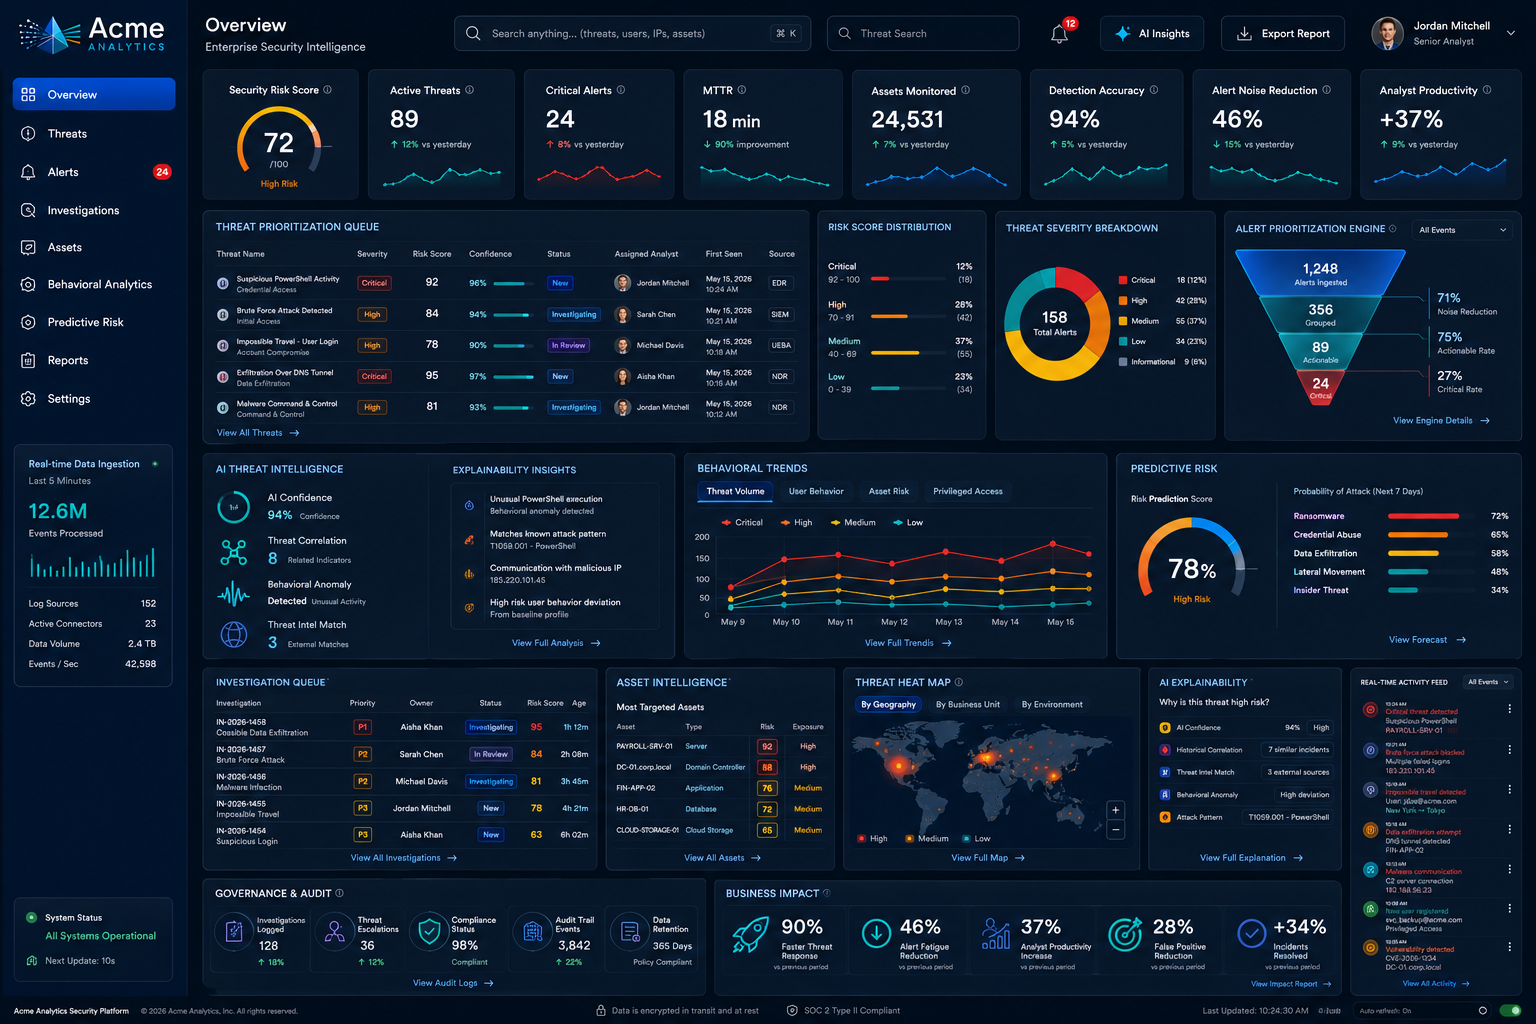
OVERVIEW
The snapshot
Challenge
Security teams were dealing with 18,000+ alerts a day from disconnected tools.
With 72% flagged as false positives, the noise buried real threats and slowed analysts down.
Approach
Led a 16-week UX research and design engagement.
Unified data, introduced AI-driven prioritization and explainability, and redesigned investigation workflows so analysts could focus on real threats.
Result
Cut alert noise by 46%, reduced mean time to respond from 2h 14m to 14 minutes, and increased analyst productivity by 37% in the first quarter.
HERO METRIC
46%
Reduction in alert noise, end to end
PROBLEM
What was breaking
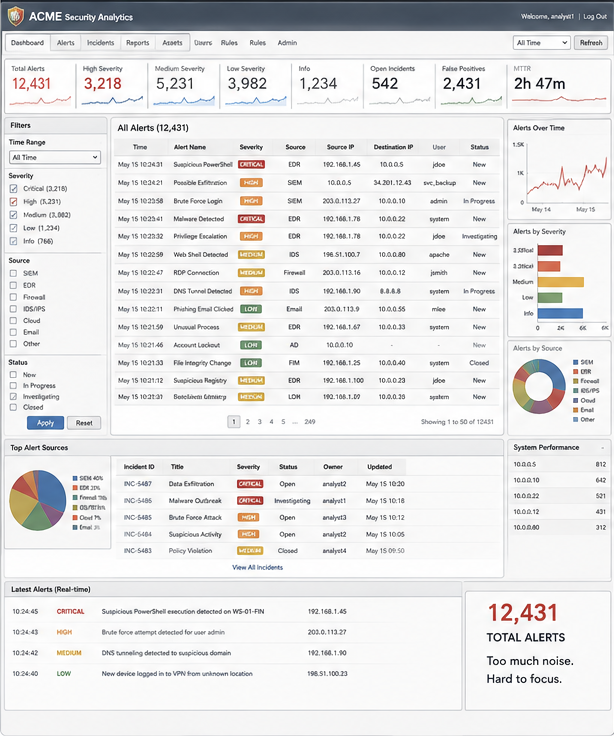
18,000+ alerts per day with 72% false positives, overwhelming analysts and hiding real threats
Analysts used 5–7 tools per investigation, spending 63% of their time switching tools instead of investigating
Escalations delayed an average of 2h 14m, letting critical threats sit unattended
We aren't short on data. We're drowning in it. — CISO, Global Enterprise
DISCOVERY
How I learned it
Discover: stakeholder alignment & tool audit
Explore: 24 analyst interviews & contextual inquiry
Observe: investigation shadowing & workflow mapping
Synthesize & validate: co-design workshops with SMEs
18,000+ alerts ingested daily, with 72% identified as false positives or low priority
Found in review of 87 SIEM rule sets & 1,248 sampled tickets
Analysts use 5–7 tools per investigation, losing context between handoffs
Found in 32 shadow sessions & 24 analyst interviews
58% of investigations involve unclear ownership, with escalations delayed 2h 14m on average
Found in document analysis & stakeholder survey
INSIGHTS
The moments things clicked
Alert overload reduces signal quality
High alert volumes and false positives overwhelm analysts and hide real threats in the noise.
Context lives across too many systems
Critical information is scattered across siloed tools, forcing analysts to piece together the full picture.
Hospitals lack real-time visibility and control
Risk scoring lacks transparency, so analysts second-guess and re-validate what the system already checked.
STRATEGY
How I chose what to build
A compliance workflow so confusing, 1 in 3 users abandoned it mid-form.
A compliance workflow so confusing, 1 in 3 users abandoned it mid-form.
A compliance workflow so confusing, 1 in 3 users abandoned it mid-form.
A compliance workflow so confusing, 1 in 3 users abandoned it mid-form.
A compliance workflow so confusing, 1 in 3 users abandoned it mid-form.
A compliance workflow so confusing, 1 in 3 users abandoned it mid-form.
THE TRADE OFF
A compliance workflow so confusing, 1 in 3 users abandoned it mid-form.
SOLUTION
The final shape of things
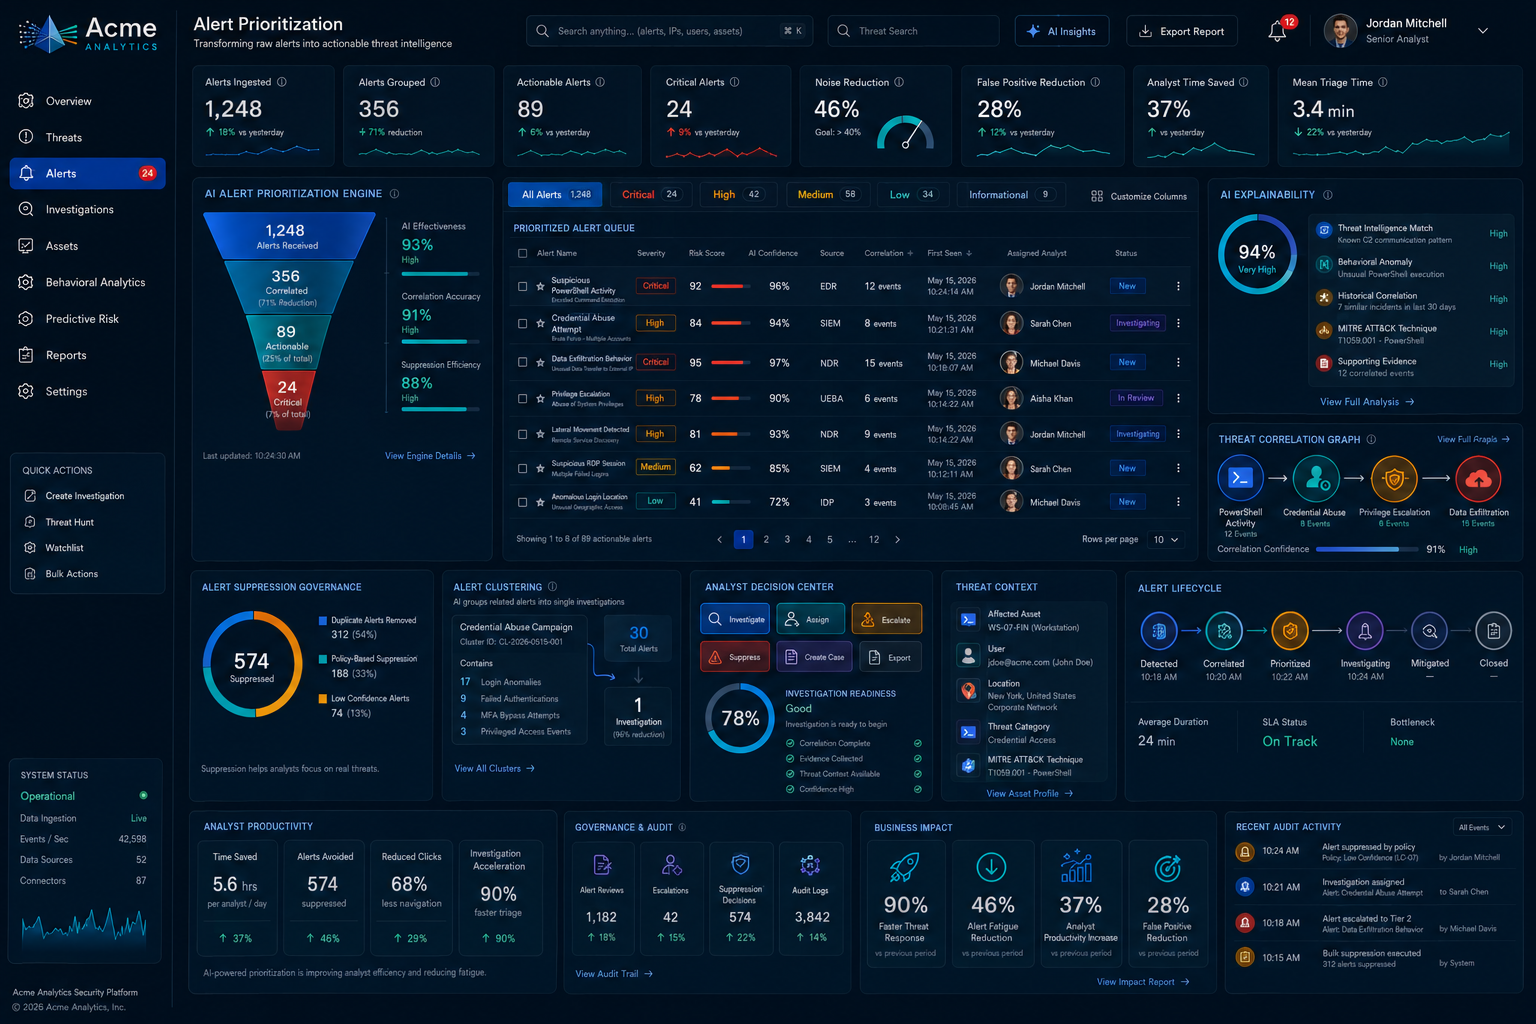
1
Risk scores analysts can actually trust
Every alert ships with a confidence score and a plain-language reason code, so analysts stop re-validating what the AI already checked.
2
One incident, not a dozen alerts
Related alerts are automatically correlated into a single incident, reducing noise by up to 70% and cutting duplicate investigation work.
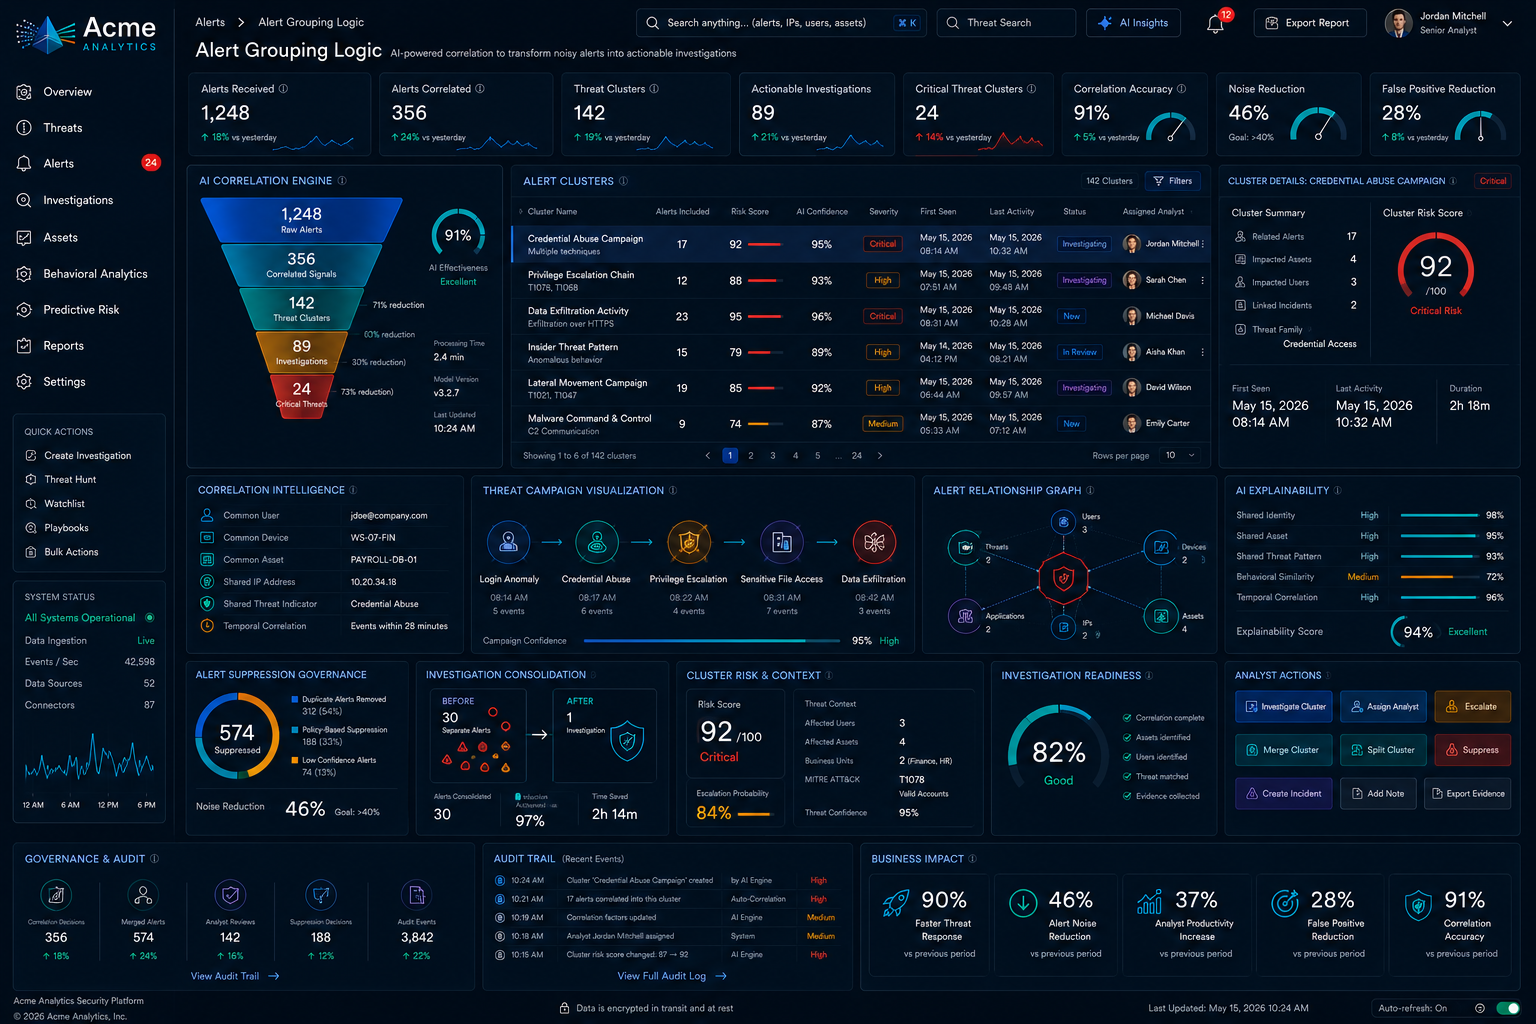
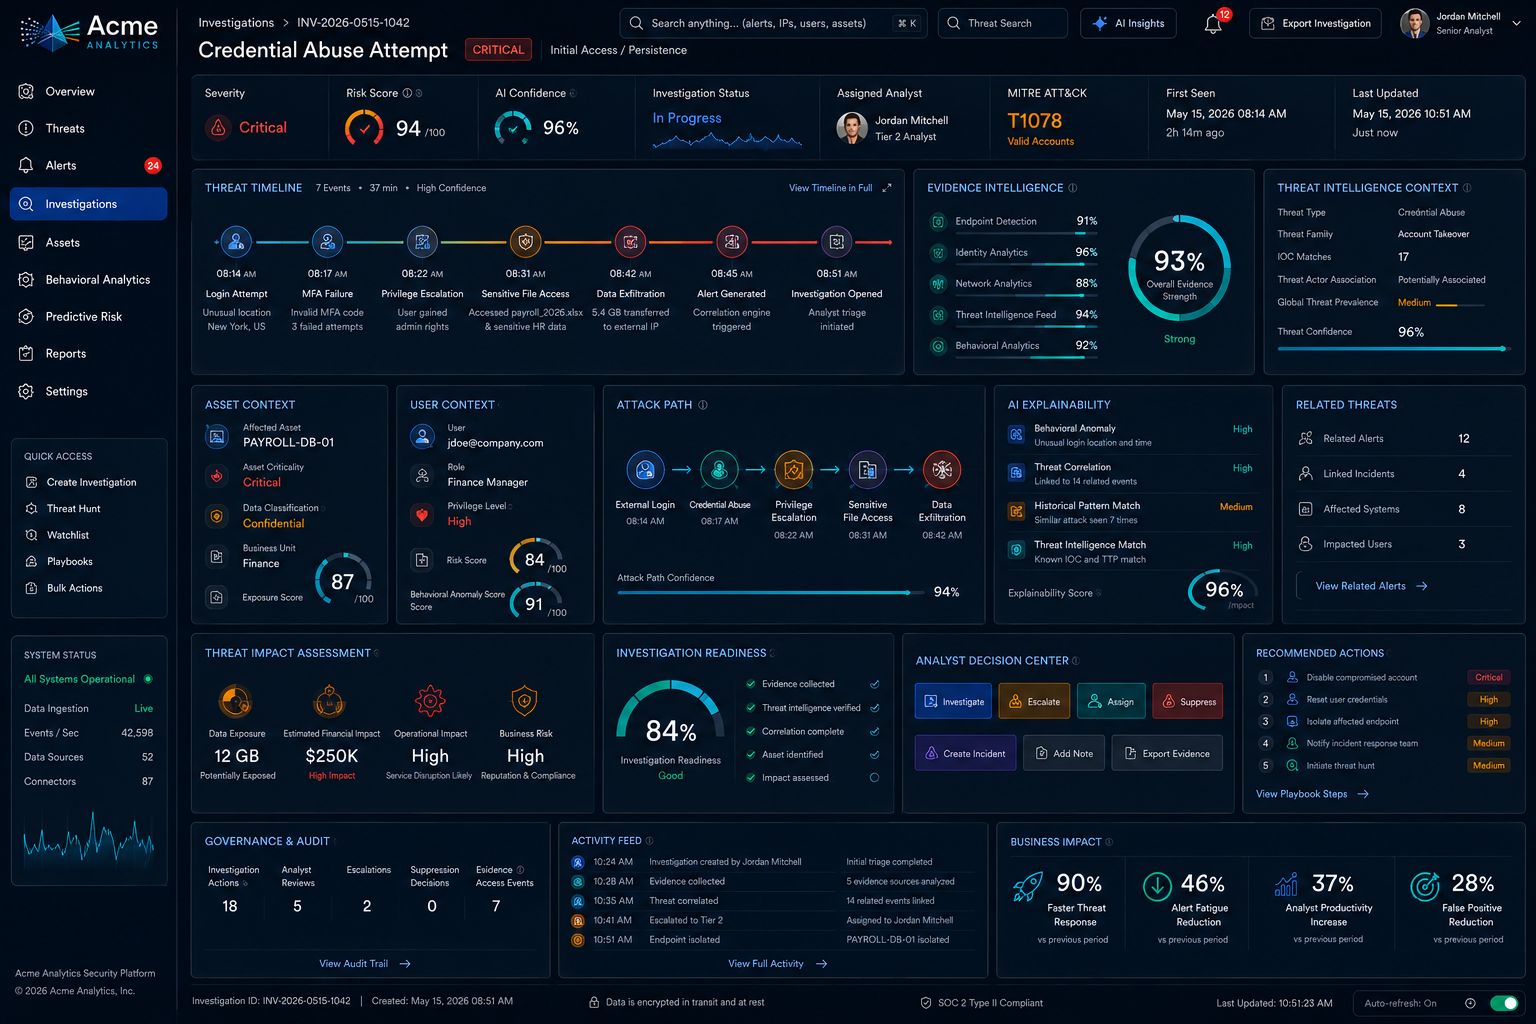
3
Every investigation, fully documented
A single investigation pane with timeline, evidence, and notes replaces scattered tickets and tribal knowledge.
IMPACT
What actually shifted

46%
Alert noise reduction

90%
Faster threat response
28%
False positive reduction

37%
Analyst productivity improvement
BEFORE
18,000+ alerts per day
2h 14m mean time to respond
12 tools in daily workflow
AFTER
9,720 alerts per day
14 minutes mean time to respond
5 tools unified into one platform
REFLECTION
What I'd carry forward
What I'd do differently
I'd bring engineering into the explainability work earlier.
Trust in the AI turned out to be as much a design problem as a modeling one, and co-designing the reason codes from week one would have saved rework.
What this taught me
Great security products don't just process more data. They help people make better decisions, faster.
The real problem wasn't the UI. It was the broken system underneath it. Fixing the system made the right interface possible.